


Tag: Linux
-
CISA has warned that attackers are actively exploiting three Linux kernel flaws, including one critical vulnerability. The agency ordered US federal organisations to patch affected systems and conduct forensic checks. CISA Adds Three Flaws to Exploited Vulnerability List The US Cybersecurity and Infrastructure Security Agency added the three vulnerabilities to its Known Exploited Vulnerabilities catalogue.…
-
Security researchers have discovered a Linux rootkit targeting F5 BIG-IP Access Policy Manager environments. The malware injects a fileless web shell directly into system memory. Therefore, it can give attackers remote access without writing the malicious PHP code to disk. Rootkit may follow exploitation of critical flaw Researchers believe attackers deploy the malware as a…
-

Tails has released an emergency update for a critical Linux kernel flaw that could allow a malicious website to take control of a user’s system and expose their identity. The privacy-focused operating system urges users to upgrade to Tails 7.10.1 immediately. Earlier versions remain vulnerable to CVE-2026-64560, a flaw that could give Tor Browser administrator-level…
-
Arch Linux contributor Robin Candau announced that package adoption has been disabled while the project investigates the situation. The restriction affects orphaned AUR packages, which are normally available for other maintainers to adopt. Attackers can exploit this process by taking over abandoned packages and adding malicious code to later releases. Users have been urged to…
-
Security researchers have disclosed a nine-year-old Linux kernel vulnerability that can allow local attackers to overwrite protected files and gain root privileges. The flaw, tracked as CVE-2026-64600 and named RefluXFS, affects the XFS filesystem when reflink support is enabled. Qualys Threat Research Unit discovered and reported the issue. The RefluXFS Linux flaw has existed in…
-
A recent Linux kernel patch designed to fix a dangerous privilege escalation flaw has reportedly introduced conditions that enabled another critical vulnerability. Security researchers warned that the new exploit, known as Fragnesia, appeared shortly after developers patched the previously disclosed Dirty Frag vulnerability. Researchers said the issue affects Linux kernel versions dating back several years…
-
New Linux kernel exploits are creating serious concerns for cloud providers and enterprise security teams after researchers disclosed two critical privilege escalation techniques affecting major Linux distributions. The flaws could allow attackers with limited system access to gain full root privileges within seconds. Researchers warned that cloud infrastructure, Kubernetes environments, and containerized workloads face elevated…
-
The Quasar Linux malware campaign is raising serious cybersecurity concerns after researchers uncovered a stealthy Linux threat designed to target software developers and DevOps environments. The malware combines backdoor access, credential theft, and rootkit functionality, allowing attackers to maintain persistent control over compromised systems. Researchers say the operation focuses heavily on development infrastructure connected to…
-
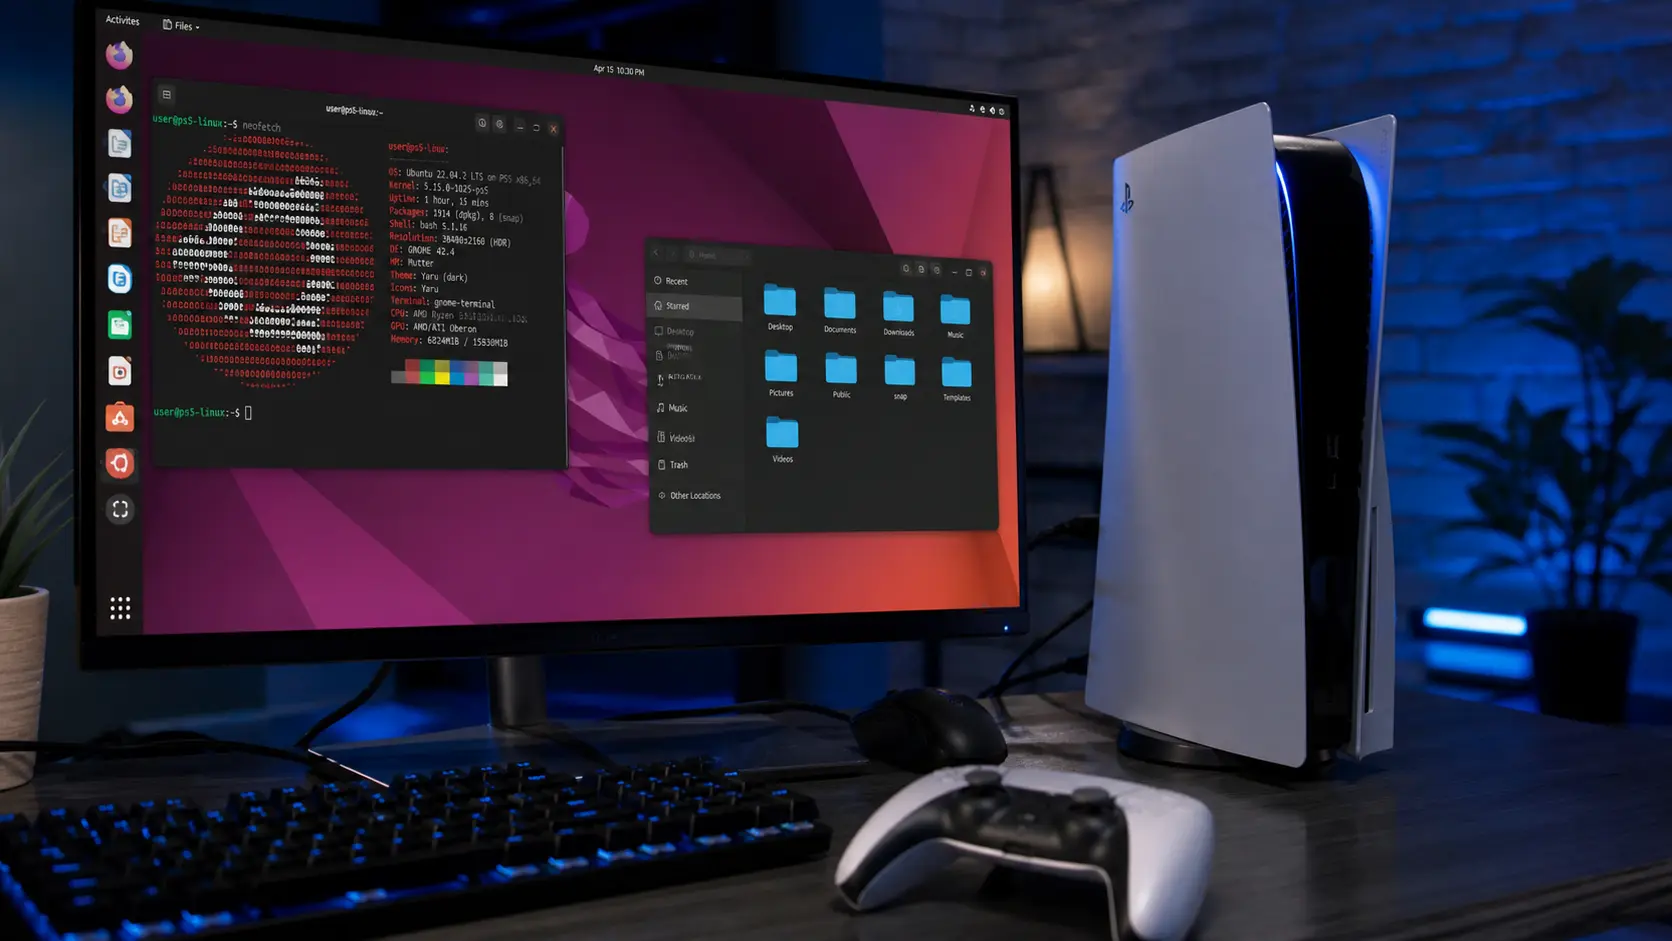
A new PS5 Linux hack is giving users access to features far beyond the console’s intended design. By leveraging a known vulnerability, the method allows the system to boot Linux and function like a full desktop environment. How the exploit works The PS5 Linux hack builds on a previously patched vulnerability discovered by security researcher…
-
A critical Linux kernel bug allows unprivileged users to gain full root access with minimal effort. As a result, the flaw creates serious risk across widely used systems. Flaw Impacts Years of Systems The vulnerability affects Linux kernels released over several years. Therefore, many environments remain exposed without immediate updates. Because the issue is not…