


Category: Cyber Security
-
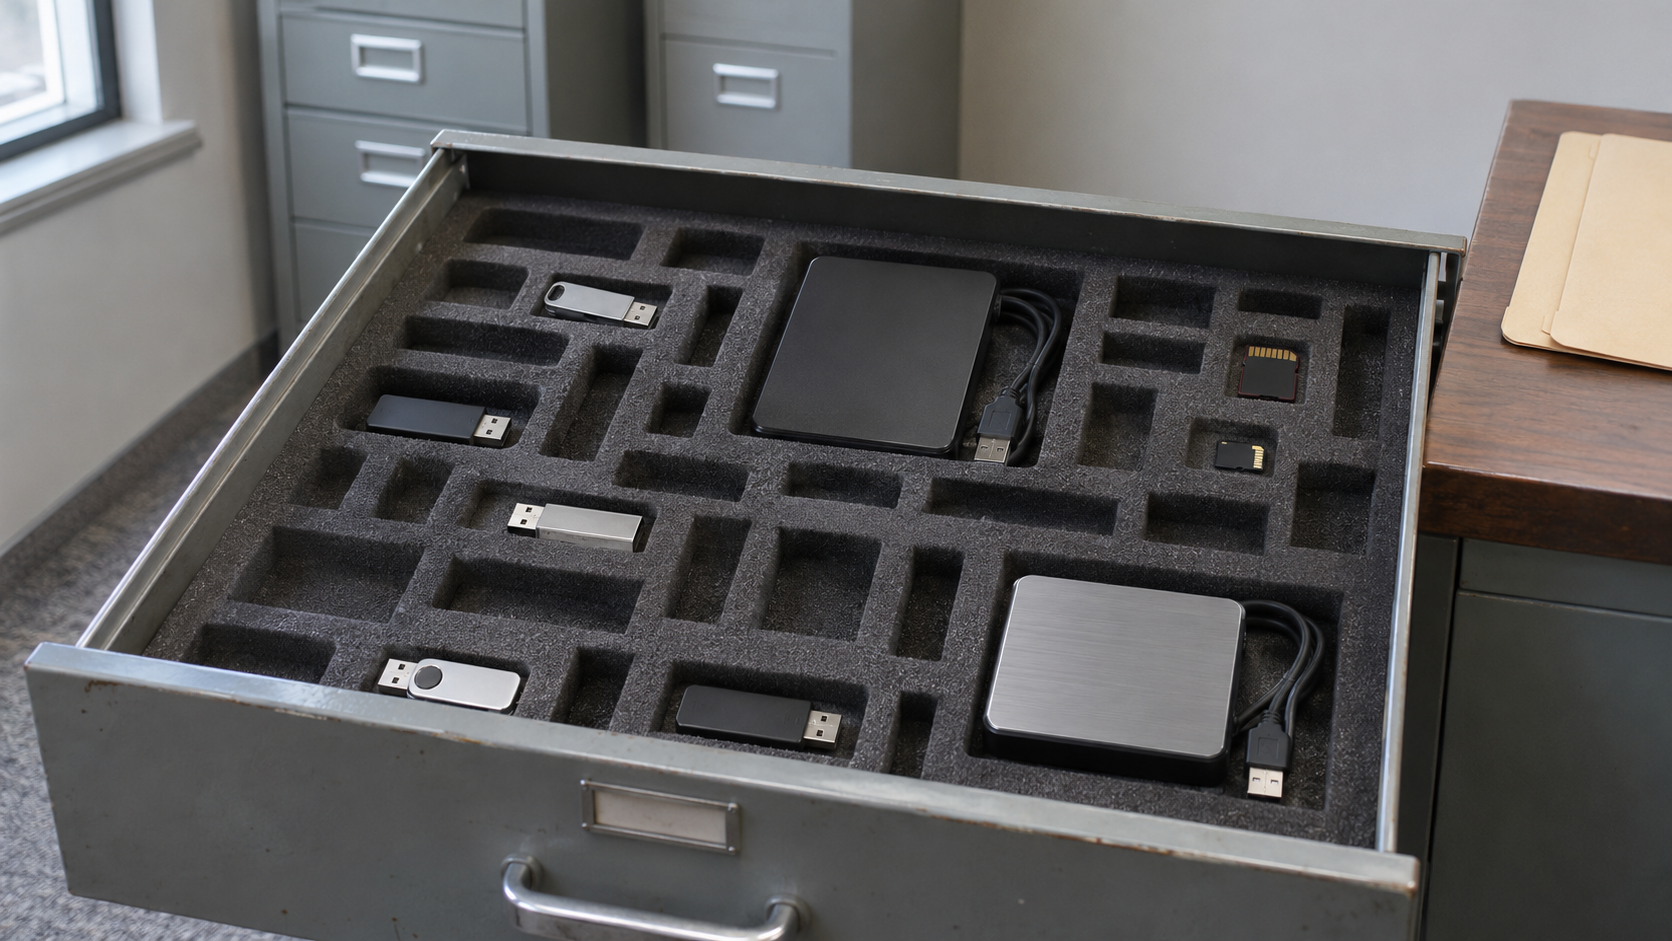
Thousands of GCHQ storage devices remain unaccounted for, according to the Investigatory Powers Commissioner’s Office (IPCO). Its 2025 annual report says the UK intelligence agency cannot immediately locate the items, some of which may contain sensitive information. Regulator identifies gaps in device tracking The equipment includes USB sticks, external hard drives, compact discs, memory cards…
-
A Sageworks outage disrupted lenders after Abrigo detected irregular activity and took the platform offline on October 30. By November 2, the company had restored most functions, although borrower-facing features remained unavailable. Abrigo shuts down platform to investigate Abrigo disabled Sageworks at approximately 11:25 a.m. Eastern Time on Friday after identifying suspicious activity in its…
-
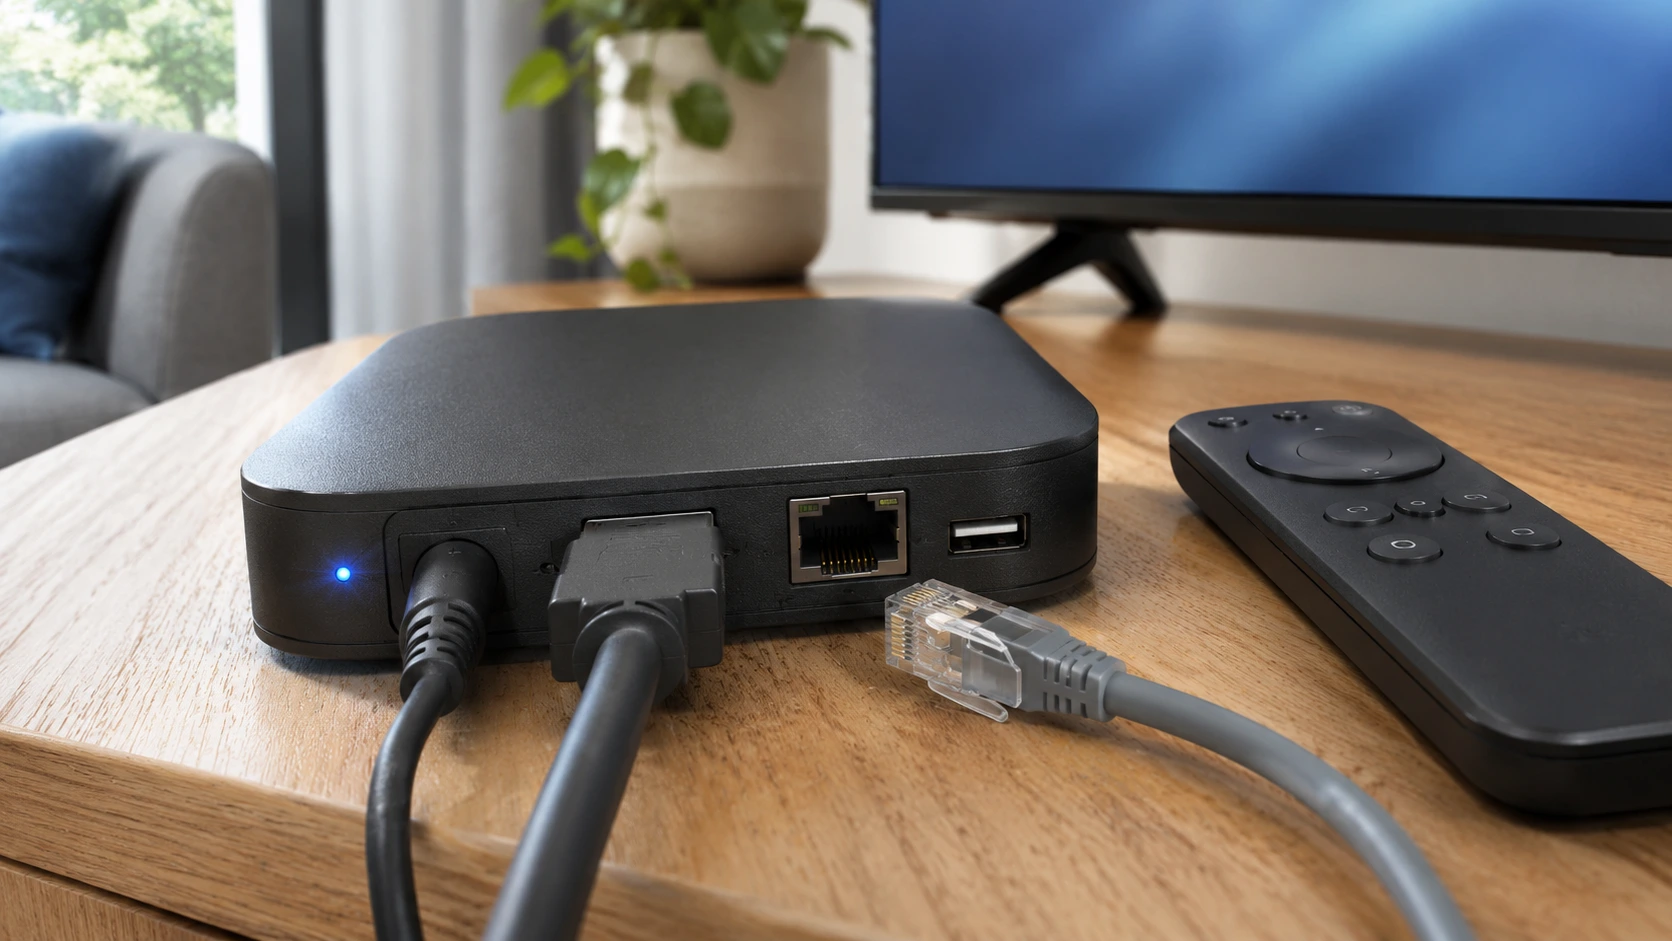
Google and its partners have disrupted the XCPE botnet, which infected more than 1.3 million Android TV streaming boxes. In its November 2 announcement, Google accused Chinese manufacturer Videostrong Technology Co. of deliberately installing malware during production and selling access to criminal affiliates. Google bans manufacturer following investigation Google said it attributed the operation to…
-
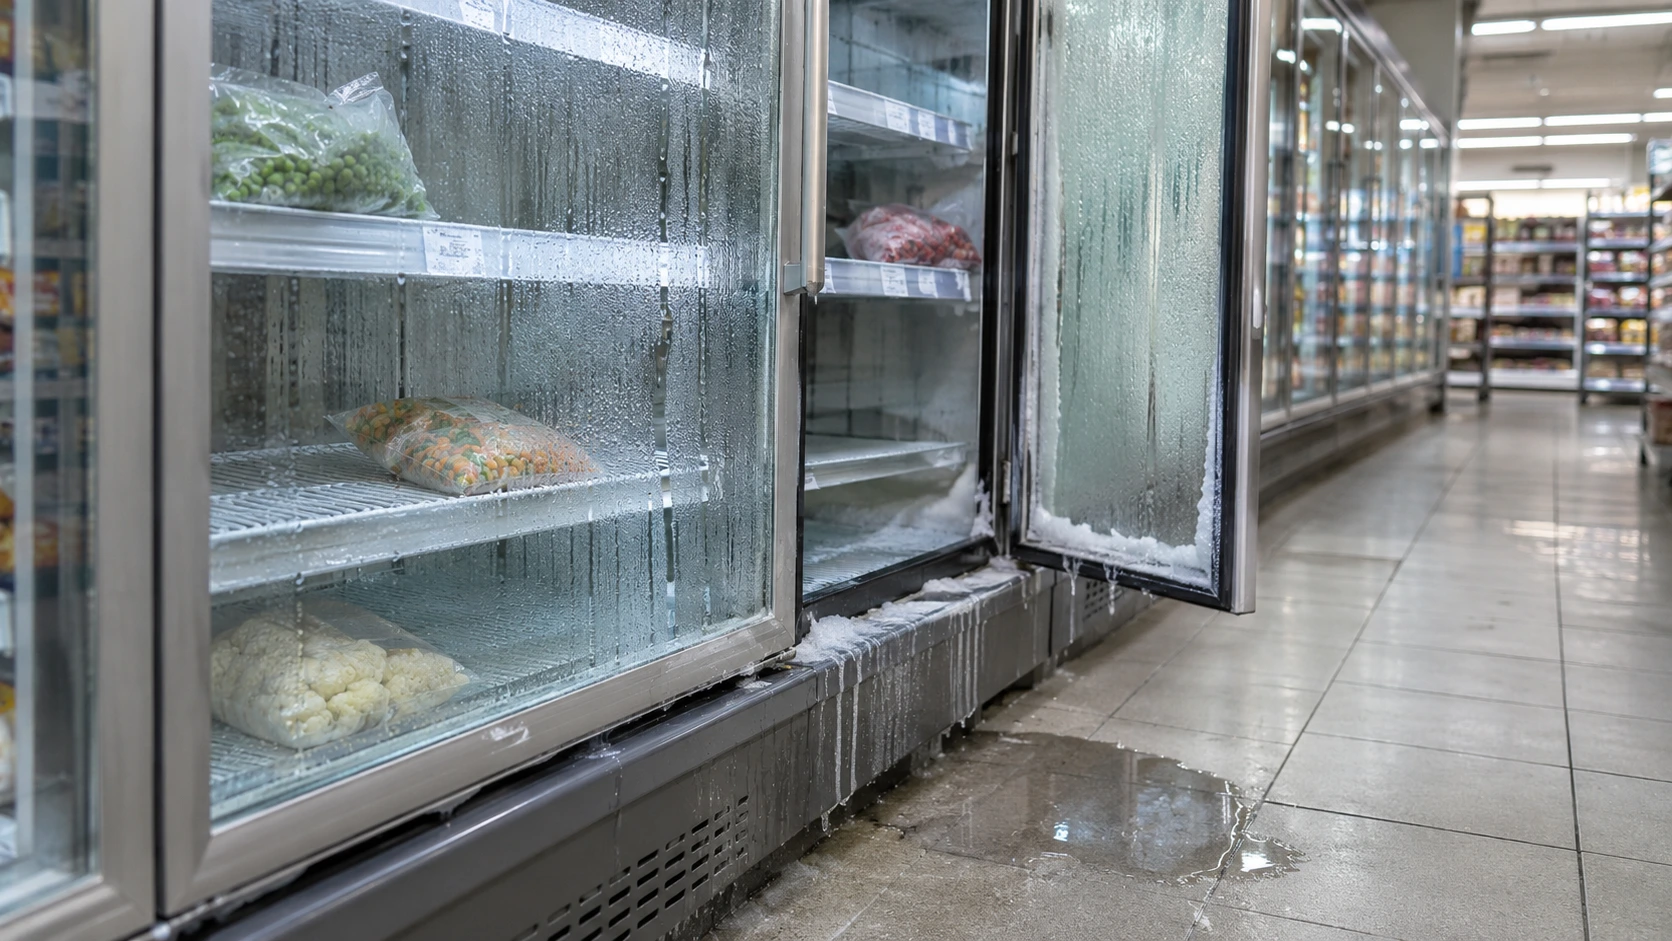
Supermarket refrigeration attacks have affected more than 115 stores across six European countries after hackers remotely altered cooling settings. The incidents forced some retailers to discard food and call managers into stores during the early morning hours on November 2. Attackers switched off refrigeration units or activated defrost functions, allowing temperatures to rise. However, investigators…
-
Microsoft has fixed a Smart App Control issue that prevented some Windows 11 users from enabling the security feature. The problem followed the October 2026 KB5127648 security update and affected devices running Windows 11 version 24H2 and later. Update Left the Security Setting Unavailable On affected computers, Windows Security displayed a greyed-out option for enabling…
-
A critical GitLab RCE flaw remains unpatched on more than 1,000 internet-accessible servers despite ongoing attacks. Shadowserver reported the exposure after GitLab released security updates on October 12, leaving administrators with an urgent patching priority. GitLab RCE Flaw Affects Pipeline Configuration Processing The vulnerability, tracked as CVE-2026-97229, involves an integer overflow in GitLab’s CI/CD Regular…
-
Synology has warned customers that C3RB3R ransomware attackers are targeting NAS devices running outdated DiskStation Manager software. The company urged users to install updates immediately after identifying attacks that exploit a vulnerability it patched in December 2024. Attackers Exploit an Older DSM Security Flaw According to Synology, the attackers aim to encrypt stored data and…
-
Ivanti zero-days have enabled attackers to compromise Connect Secure remote access gateways by combining three vulnerabilities. The company has now patched two additional flaws linked to attacks dating back to at least October 1, 2026. Two Additional Vulnerabilities Complete the Attack Chain The newly addressed vulnerabilities are CVE-2026-111357 and CVE-2026-118527. The first allows high-severity privilege…
-
Alpine Linux rebuilt its GitLab server and reset all user passwords after attackers targeted a critical vulnerability on October 20–21. Although investigators found no evidence of successful code execution, missing logs prevented them from ruling out a compromise. Attackers Target Alpine Linux Development Infrastructure The attacks focused on CVE-2026-97229, a maximum-severity remote code execution vulnerability…
-
An invisible SMS of Death attack can interrupt Android phone calls and leave vulnerable devices stuck in repeated crashes, security researcher Mark Blaszczyk warns. His findings describe an attack that requires no user interaction and could force affected owners to reset their phones. Hidden Messages Crash Android’s Phone Service The vulnerability involves WAP Push, a…