


Category: Cryptocurrencies
-
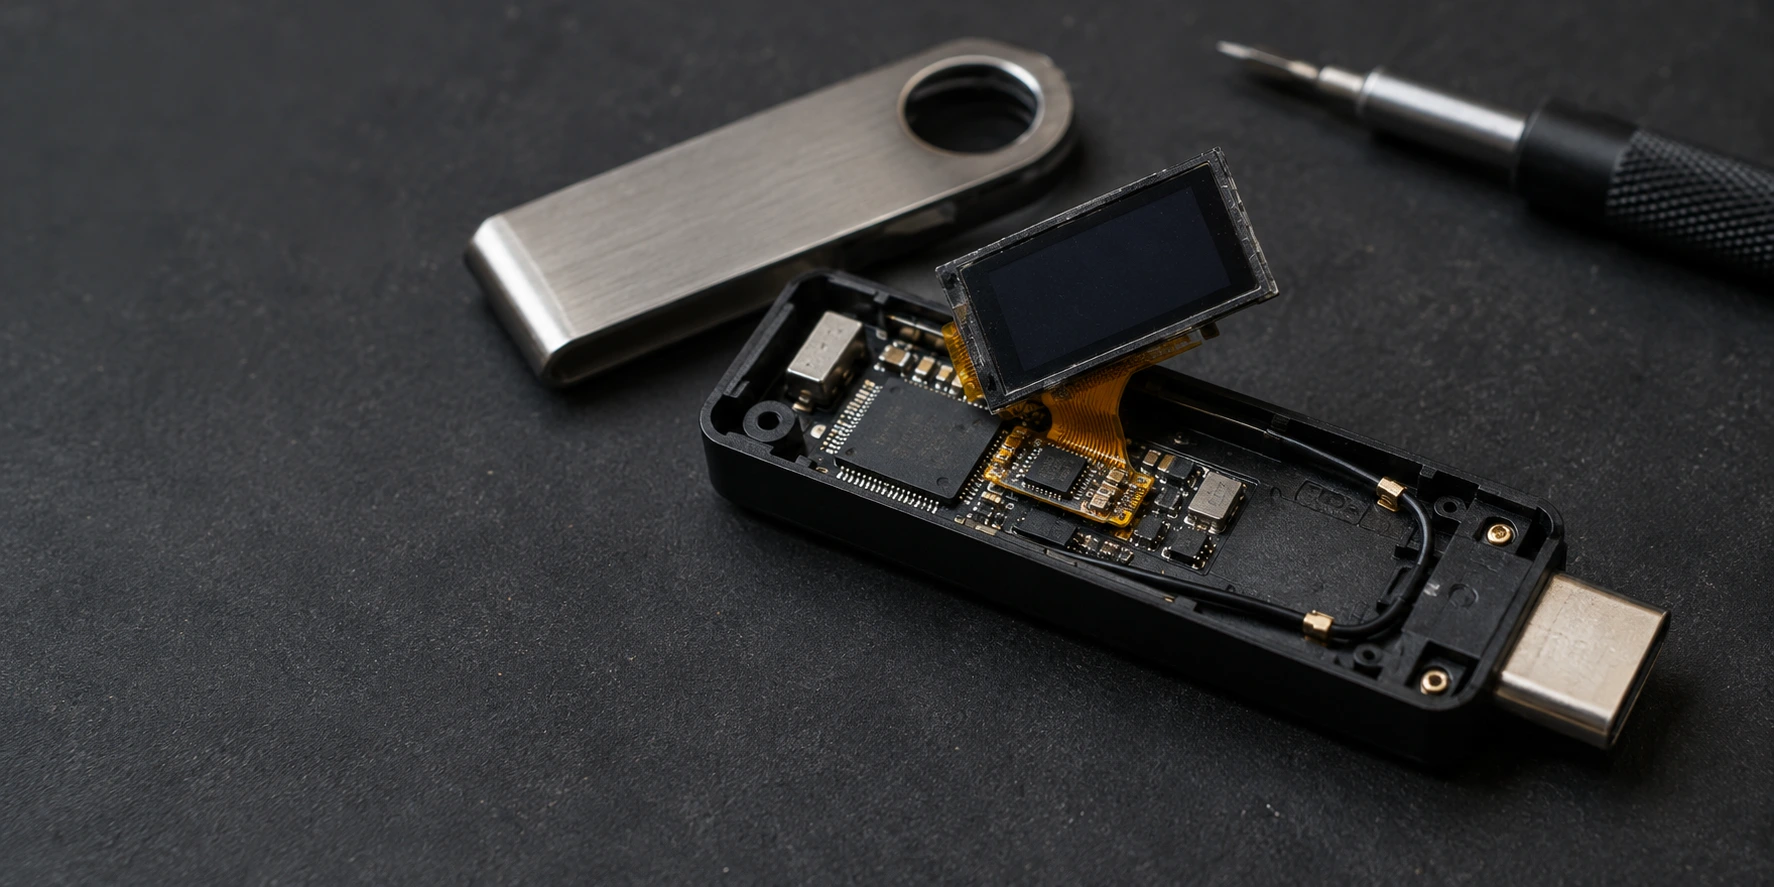
Ledger has confirmed that an unauthorized Ledger hardware implant was present in a device linked to reported cryptocurrency thefts. The investigation centers on wallets sold through CryptoBilis, a Malaysia-based reseller operating across Southeast Asia. According to Ledger, all unexpected fund-drain reports received during its investigation involved devices from that reseller. The company described the affected…
-
A UK man has received a two-and-a-half-year prison sentence for SIM-swap fraud linked to cryptocurrency thefts totaling nearly £200,000, approximately $265,000. Police said he used his share of the proceeds to finance luxury holidays and expensive purchases. Ajay Shinjin, 25, also known as AJ Marley Cruz, pleaded guilty at Inner London Crown Court on September…
-
Canadian cybersecurity executive Edward Dubrovsky faces conspiracy and extortion-related charges after authorities arrested him in Pennsylvania. Reports have connected the Edward Dubrovsky arrest to the ShinyHunters investigation, although the FBI has not publicly confirmed that link. Dubrovsky, 54, has held senior positions at companies that help organizations respond to ransomware and negotiate extortion payments. He…
-
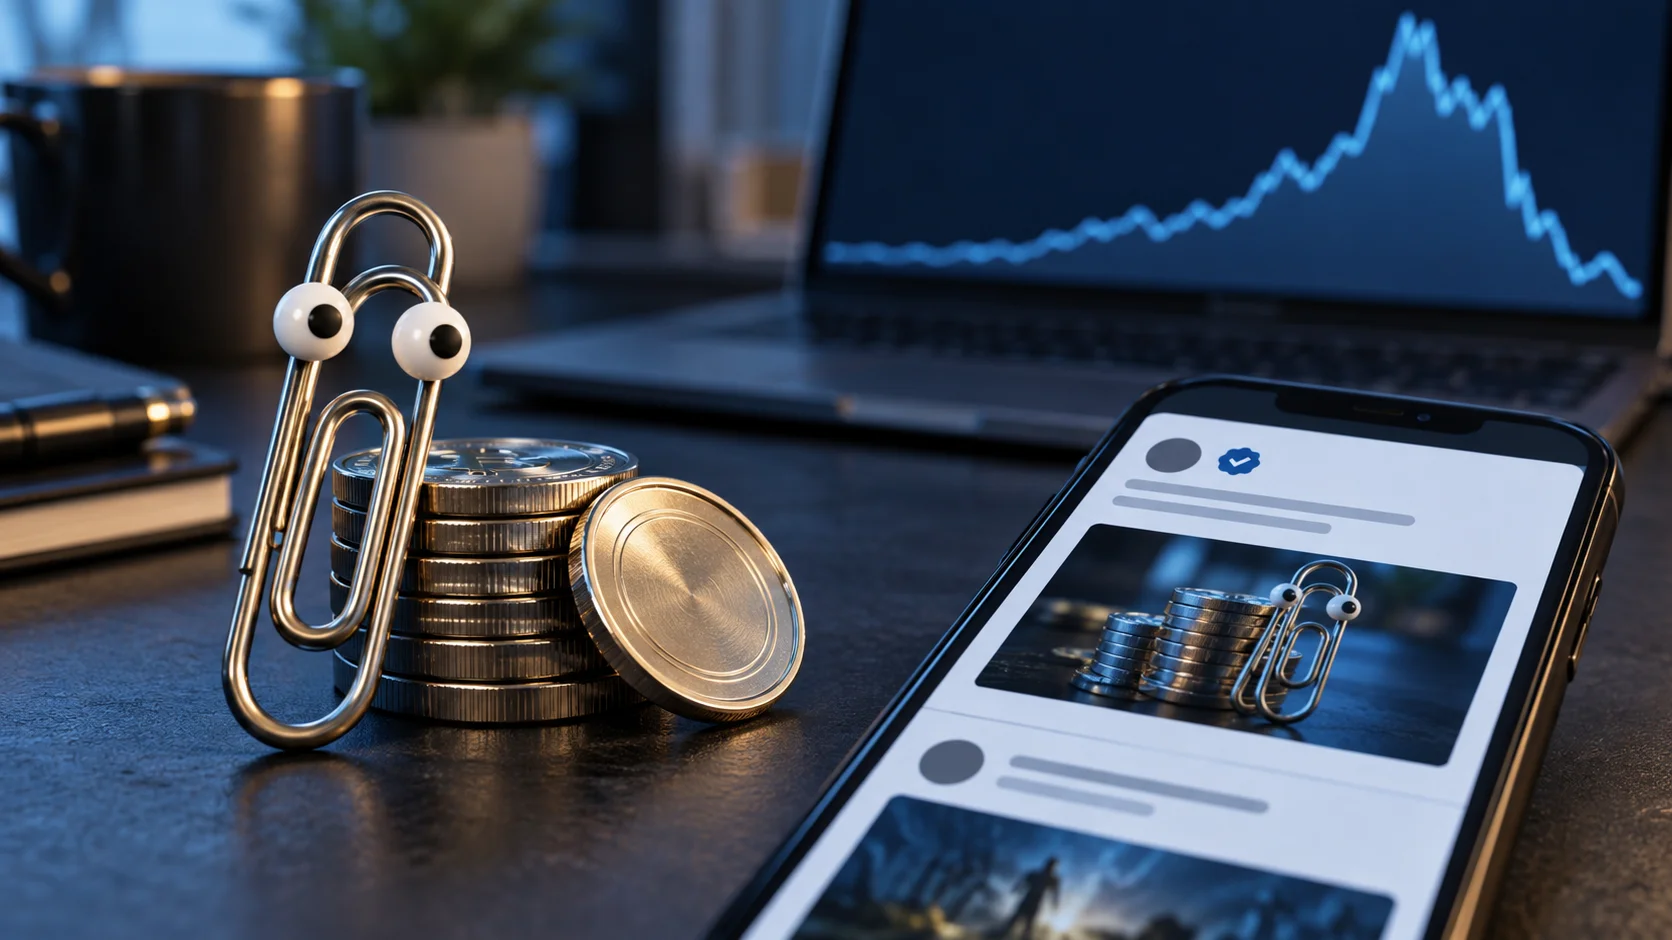
Microsoft has secured its official X account after attackers used it to promote an unauthorized cryptocurrency token linked to its Clippy character. The Microsoft X hack affected an account with more than 13 million followers, giving the promotion a large potential audience. The company confirmed that someone accessed the account without permission and published posts…
-
Russian state-linked hacking group Star Blizzard has adopted a delivery method that automates more of its malware installation process. Microsoft researchers say RedFlick malware attacks use deceptive file attachments to install the group’s CosmicPulse backdoor. The approach still depends on phishing and a victim opening a malicious file. However, it requires fewer manual steps than…
-
A Vietnamese national faces money laundering charges over an alleged crypto investment scam that cost one victim approximately $16 million. Prosecutors say cryptocurrency transfers link the victim’s losses to wallets controlled by 37-year-old Trung Nguyen Van. Authorities Arrest Suspect at Los Angeles Airport Van entered the United States through the San Ysidro pedestrian border crossing…
-
Bitget Bitcoin withdrawals have resumed after a cyberattack that stole $387.5 million from the cryptocurrency exchange. The company says it has fixed the exploited vulnerability and plans to restore withdrawals for other assets in stages. Bitget attributes the attack to suspected North Korean hackers. However, that attribution rests on the company’s analysis rather than an…
-
A new MacSync malware campaign uses public iCloud calendar events as part of its infection chain, according to Kaspersky researchers. Commands hidden in an event description direct a downloader to fetch more malicious components from iCloud. Calendar Event Hides Download Commands MacSync targets macOS users through deceptive downloads and social engineering. Researchers have seen it…
-
CISA has warned that hackers are actively exploiting a maximum-severity GitLab vulnerability. The flaw allows unauthenticated attackers to read credentials, secrets and other sensitive files from vulnerable servers. Tracked as CVE-2026-85706, the security issue affects GitLab Community Edition and Enterprise Edition. Administrators should install the available updates immediately and inspect their logs for signs of…
-
A massive online fraud network known as DoppelCart operates more than 119,000 fake stores designed to steal payment card information. Most of the fraudulent domains use the .SHOP top-level domain. In fact, the network accounts for approximately 2.72 percent of all websites registered under that domain extension. German cybersecurity company Nebty discovered the operation. It…