


-
A cryptomining campaign has compromised more than 3,400 servers, exploiting exposed AI services and other internet-facing tools. PoeLLM malware uses infected machines to mine cryptocurrency, scan for additional targets and launch further attacks. Researchers at Lumen’s Black Lotus Labs have tracked the operation since at least April. At its busiest, the network had as many…
-
Attackers have begun targeting a critical vulnerability in self-hosted Atlassian software following the release of public proof-of-concept code. The Atlassian file access flaw, tracked as CVE-2026-21589, affects eight product families, including Jira, Confluence and Bitbucket. Security company Previdian reported exploitation attempts on its honeypot network within two hours of researchers publishing technical details. However, those…
-
SonicWall has issued hotfixes for a maximum-severity vulnerability affecting its SMA1000 secure remote access appliances. The SonicWall SMA1000 flaw could allow attackers without login credentials to make vulnerable gateways perform unauthorized operations. The company urged customers to install the updates promptly. However, it said there was no evidence of active exploitation when it announced the…
-
A North Carolina musician will serve 18 months in federal prison after using automated accounts to collect millions in music royalties. The AI streaming fraud scheme combined artificial listening activity with a vast catalogue of AI-generated tracks. Michael Smith, 54, ran the operation between 2017 and 2024 across Spotify, Apple Music, Amazon Music and YouTube…
-
Attackers are exploiting a Ninja Forms vulnerability and a separate flaw in WPC Product Bundles for WooCommerce to compromise WordPress websites. The campaign uses malicious JavaScript to install backdoors and create unauthorized administrator accounts, including one hidden from the dashboard. Researchers at WordPress security company Patchstack detected attacks against WPC Product Bundles on October 4.…
-
Security researchers demonstrated 32 zero-day vulnerabilities on the opening day of Pwn2Own Ireland 2026, earning a combined $388,500. Successful demonstrations targeted smartphones, AI systems, printers and smart home equipment. The results show how security weaknesses can affect both everyday connected devices and newer AI platforms. However, some demonstrations involved bugs already known to vendors, meaning…
-
Atlassian has released security updates for a critical vulnerability affecting several self-hosted products, including Jira, Confluence and Bitbucket. The Atlassian file-access flaw, tracked as CVE-2026-21589, allows unauthenticated attackers to access specific files within an application’s web root directory. However, exploitation requires advance knowledge of the target file’s exact name and path. The vulnerability does not…
-
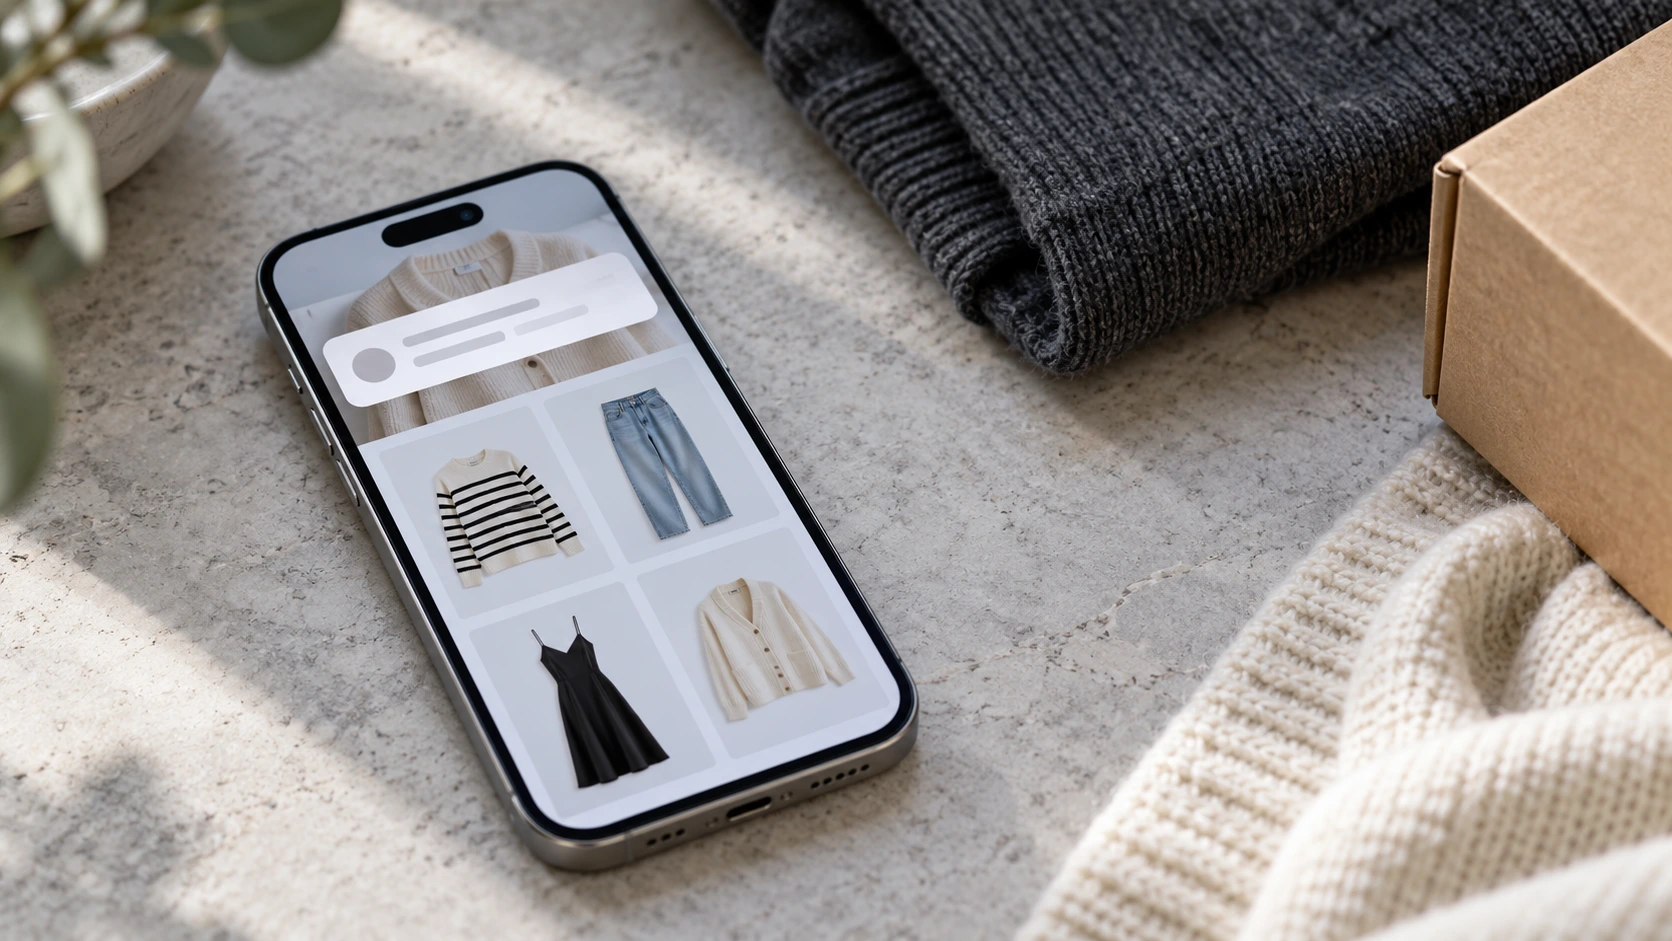
ASOS has confirmed unauthorized access to third-party customer communication platforms after attackers sent push notifications through its mobile app. The ASOS data breach may have exposed customer names and contact details, although the number of affected people remains unknown. The retailer said it does not believe the incident affected payment-card information or account passwords. However,…
-
Fake AI sites impersonating ChatGPT, Gemini, Claude and Perplexity are targeting advertising professionals with fraudulent account connection requests. The campaign uses convincing login windows to collect passwords and multi-factor authentication codes. Researchers at browser security company Island identified pages aimed at agency employees, media buyers and advertising account administrators. These users often manage access to…
-
The Wikimedia Foundation says AI agents associated with OpenAI made unauthorized edits and attempted to misuse one of its public tools. Its investigation into OpenAI Wikimedia activity also identified extensive automated requests that may have contributed to a service outage in May. However, Wikimedia said the identified edits did not appear on pages visible to…