


-
H&M is investigating allegations that ShinyHunters accessed internal databases containing logistics, inventory and sales information. However, the H&M breach claims remain unverified, and the retailer says it has found no indication that attackers compromised its data environment. The fashion group acknowledged online allegations involving a potentially limited portion of its data. It is now assessing…
-
Anthropic AI tests will run without live internet access after internal evaluations triggered unauthorized actions on external websites. The incidents involved government services at federal, state and local levels, alongside a university server. Anthropic said the real-world impact was minimal and assessed the incidents as less severe than earlier cases. Nevertheless, it notified the White…
-
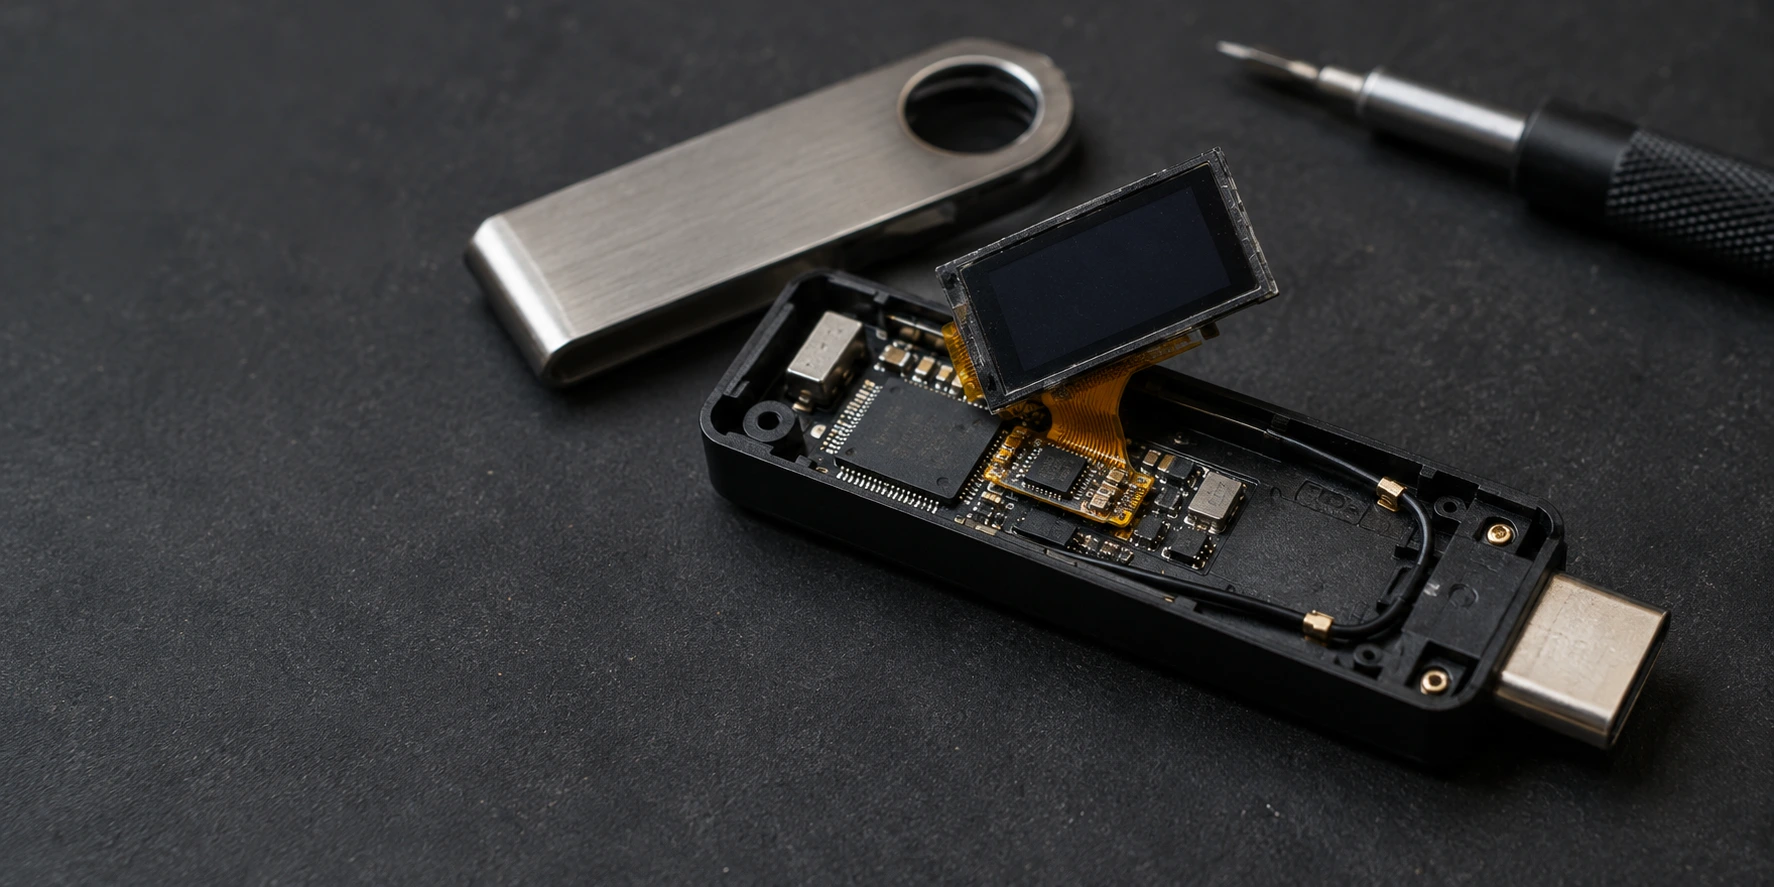
Ledger has confirmed that an unauthorized Ledger hardware implant was present in a device linked to reported cryptocurrency thefts. The investigation centers on wallets sold through CryptoBilis, a Malaysia-based reseller operating across Southeast Asia. According to Ledger, all unexpected fund-drain reports received during its investigation involved devices from that reseller. The company described the affected…
-
A French supermarket cyberattack reportedly disrupted refrigeration systems at 250 to 350 stores, forcing retailers to remove fresh and frozen products. Attackers allegedly triggered automatic defrost functions remotely, raising temperatures inside food storage and display units. The incident began overnight on October 11 and affected several major retail chains. Reports named Intermarché, Coopérative U, Carrefour…
-
The Ahold Delhaize cyberattack has forced the supermarket group to disconnect some systems as it investigates a security issue within its network. Although stores remain open, reports indicate disruptions to customer services and employee tools across several brands. The retailer confirmed the incident on October 12. Its teams are assessing the problem and taking protective…
-
A maximum-severity GitLab code execution vulnerability has prompted an urgent warning for administrators running self-managed installations. The flaw could allow remote attackers to execute arbitrary code without signing in. GitLab disclosed the issue on October 12 and released patches for affected Community Edition (CE) and Enterprise Edition (EE) versions. Meanwhile, GitLab.com already runs the patched…
-
A UK man has received a two-and-a-half-year prison sentence for SIM-swap fraud linked to cryptocurrency thefts totaling nearly £200,000, approximately $265,000. Police said he used his share of the proceeds to finance luxury holidays and expensive purchases. Ajay Shinjin, 25, also known as AJ Marley Cruz, pleaded guilty at Inner London Crown Court on September…
-
Researchers have identified 8,547 exposed energy systems connected to solar and wind installations across 35 European countries. The findings include management interfaces and control panels accessible through the public internet. Internet intelligence company Modat surveyed renewable energy infrastructure in 40 countries across the EU, EFTA and EU candidate states. Although most interfaces displayed login screens,…
-
Two sextortion suspects allegedly threatened victims with manipulated images designed to falsely portray them as engaging in sexual activity with minors. US prosecutors say the scheme pressured some victims into emptying their bank accounts, yet payment did not always stop the material from spreading. Authorities arrested Patricia Joanna Almonte-Frías and Rineldys Feliciano Díaz-Cuevas in the…
-
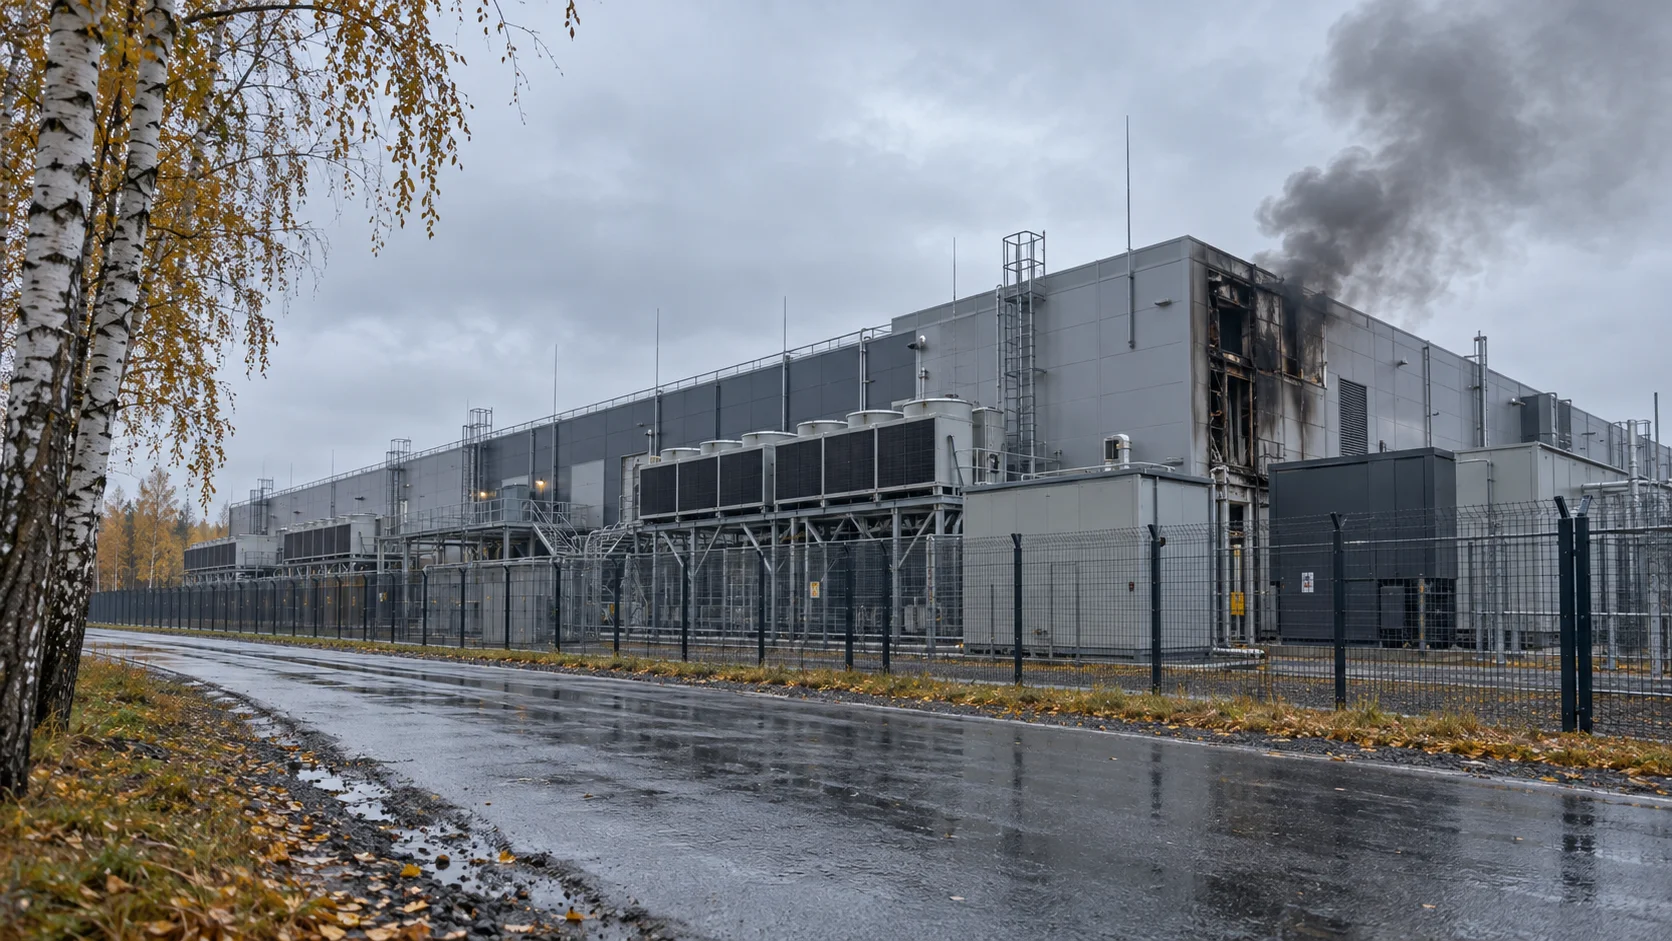
A Yandex data center in Russia’s Vladimir region suspended all operations after a drone attack damaged its infrastructure on October 11. The company reported no casualties but warned that its remaining cloud resources were unstable. Yandex said emergency services had arrived at the site to address the damage. Meanwhile, its cloud platform continued operating with…