


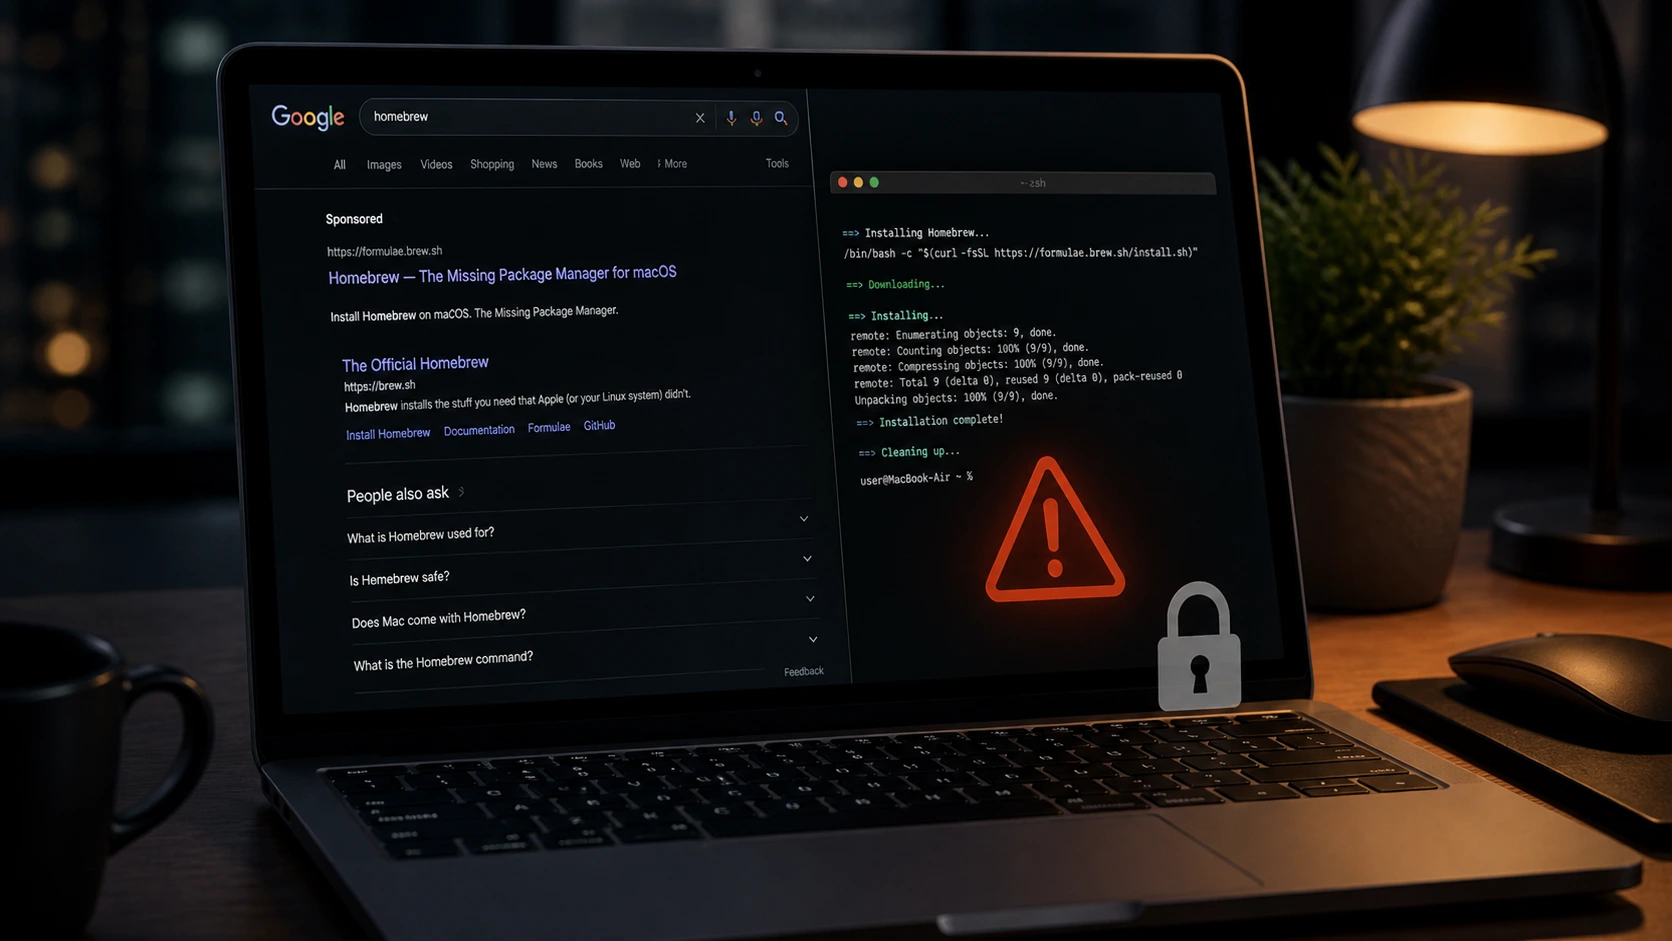
Security researchers have uncovered a homebrew malvertising campaign that targets macOS users through Google Search ads. Attackers place fake sponsored results above legitimate links, making malicious pages look trustworthy at first glance.
This method relies on user behavior. Many users click the first result without verifying the source. As a result, attackers can redirect victims to cloned websites that closely mimic the official Homebrew platform.
Fake Google Ads Drive the Attack
The homebrew malvertising campaign uses sponsored ads to push malicious links to the top of search results. These ads often appear identical to legitimate listings, which increases the chance of user interaction.
Attackers also rely on compromised advertiser accounts to run these campaigns. This tactic helps them bypass standard ad verification systems. In some cases, they host fake pages on trusted platforms, which adds another layer of credibility.
The cloned websites replicate the design and content of the real Homebrew site. For most users, the differences are difficult to detect without careful inspection.
Malicious Commands Install Infostealer
The infection chain in the homebrew malvertising campaign begins with a familiar instruction. Users are asked to copy and paste a command into the macOS terminal, similar to the official installation process.
However, the command has been altered. Instead of installing the package manager, it downloads an infostealer. The malware then collects sensitive data from the system, including stored credentials and system details.
Once executed, the payload sends the stolen data to a remote server controlled by attackers. The process may end with an error message, which helps hide the malicious activity.
Trusted Tools Increase Success Rates
The homebrew malvertising campaign succeeds because it targets a widely trusted developer tool. Homebrew is commonly used in the macOS ecosystem, which makes users less likely to question the installation steps.
This approach reflects a broader trend in cybercrime. Attackers increasingly impersonate trusted brands to deliver malware. By aligning attacks with normal workflows, they reduce suspicion and improve success rates.
Similar tactics have targeted other popular software tools, showing that this method is scalable and effective.
Malvertising Remains a Growing Threat
Malvertising continues to evolve as attackers refine their techniques. Instead of exploiting technical vulnerabilities, they focus on manipulating user trust and platform systems.
This strategy allows campaigns to reach large audiences quickly. It also makes detection more difficult, especially when attackers use legitimate services to host their content.
The homebrew malvertising campaign demonstrates how effective this approach can be against both casual users and developers.
Conclusion
The homebrew malvertising campaign shows how attackers combine social engineering with trusted platforms to deliver malware. By abusing Google ads and cloning legitimate websites, they create convincing entry points for infection.
Users can reduce risk by avoiding sponsored links when downloading software and verifying official sources. As these campaigns become more advanced, awareness remains a critical defense.
0 responses to “Homebrew Malvertising Targets Mac Users via Google Ads”