


Category: Cyber Security
-
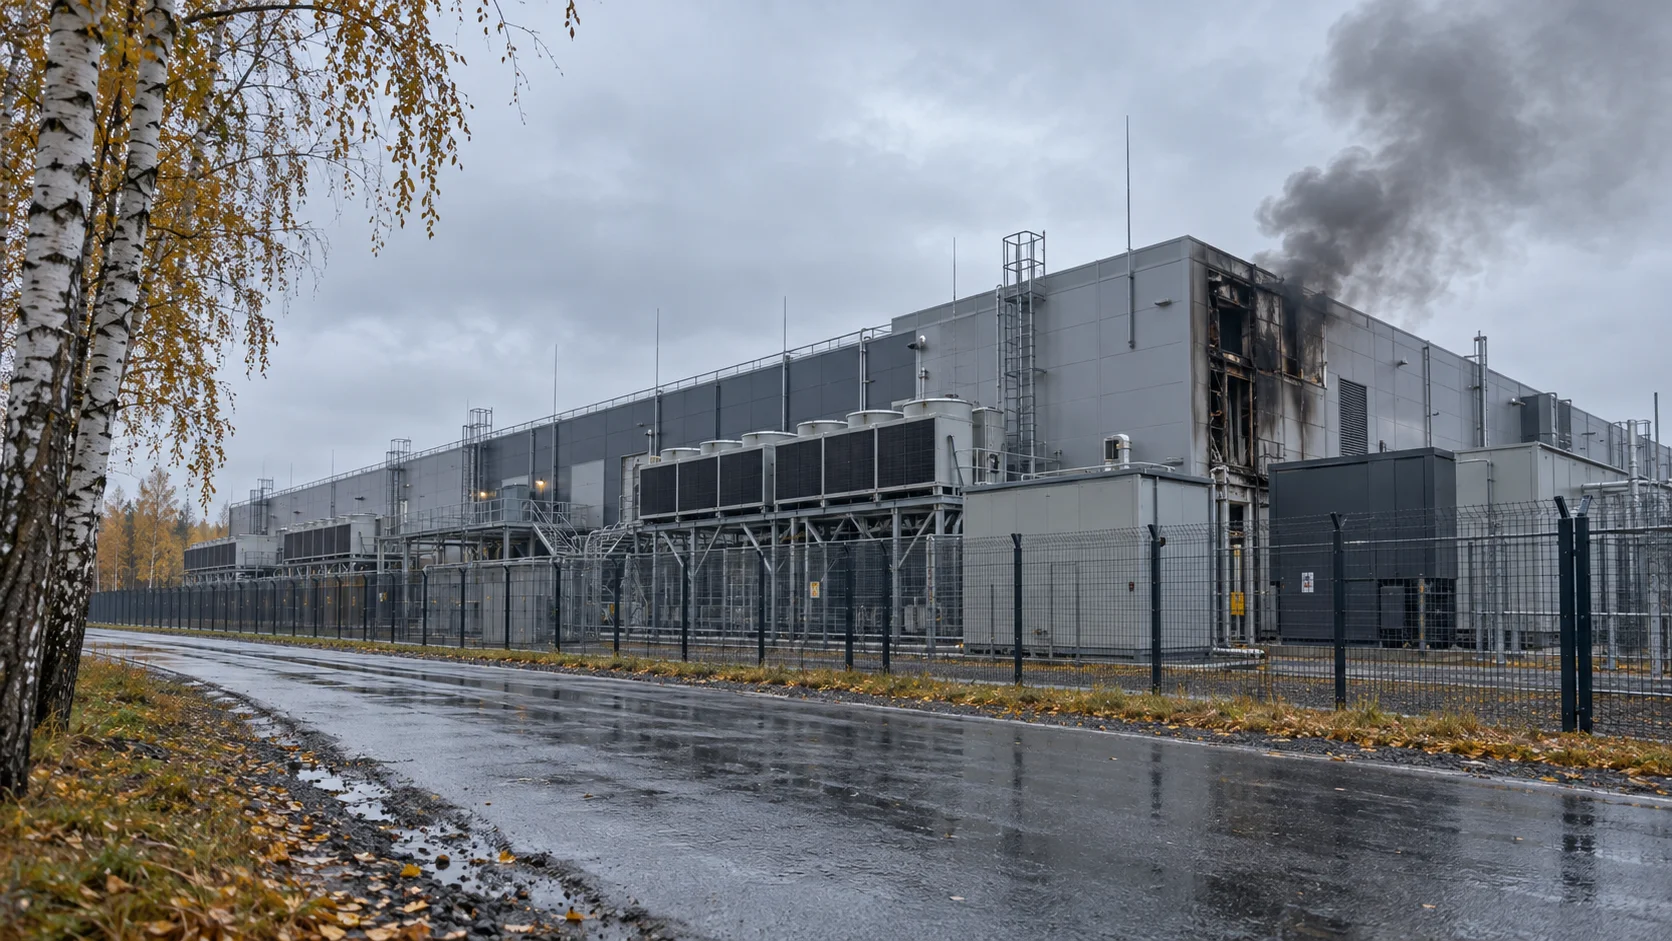
A Yandex data center in Russia’s Vladimir region suspended all operations after a drone attack damaged its infrastructure on October 11. The company reported no casualties but warned that its remaining cloud resources were unstable. Yandex said emergency services had arrived at the site to address the damage. Meanwhile, its cloud platform continued operating with…
-
The IDCF Cloud attack has affected 495 companies and local government services in Japan, according to cloud provider IDC Frontier. The disruption has reached railway businesses, food logistics and other services, while some customers face potentially unrecoverable data loss. The SoftBank-owned provider said attackers knocked servers offline in the early hours of Wednesday, October 7.…
-
Attackers are exploiting two AhsayCBS security flaws to compromise backup management servers, install webshells and run cryptocurrency miners. Researchers observed the activity on October 7, with at least five organisations targeted. Although vulnerability records list both issues as fixed in version 10.3.2, Huntress found that they also affect version 10.3.4. That was the latest release…
-
German authorities have arrested a Russian national suspected of holding a leading role in the Qilin ransomware operation. The Qilin ransomware arrest follows the suspect’s extradition from Japan earlier this month. Japan’s National Police Agency confirmed that authorities detained the man after he entered the country as a tourist. Germany had sought his arrest in…
-
Oleg Korniev has pleaded guilty to helping lead a money mule network that moved stolen funds for cybercriminals worldwide. The operation used more than 15,000 US recruits, many of whom believed they had accepted legitimate payment-processing jobs. The 42-year-old Ukrainian-Russian dual citizen admitted his role in Your Mule Cashout, known as YMCO. His guilty plea…
-
Citrix has urged administrators to immediately patch a critical NetScaler RCE flaw affecting NetScaler ADC and NetScaler Gateway. The vulnerability could allow attackers to execute code remotely or crash affected appliances. Tracked as CVE-2026-107406, the issue stems from a memory overflow weakness. However, exposure depends on configuration: appliances must operate as a SAML Identity Provider…
-
Security researchers earned $1,262,000 at Pwn2Own Ireland 2026 after demonstrating 98 zero-day vulnerabilities over three days. The competition tested smartphones, AI products and other connected technologies through controlled hacking attempts. Ikotas Labs finished first with 42.5 Master of Pwn points and $361,000 in rewards. Its successful demonstrations included the Samsung Galaxy S26, OpenAI Codex, Oracle…
-
The FBI has seized seven domains supporting hacking tools allegedly used by Chinese state-sponsored attackers to compromise organizations worldwide. The Flax Typhoon disruption targeted infrastructure behind MicroScan and FishHub, two platforms linked to vulnerability scanning, network intrusions and data theft. U.S. authorities attribute the platforms to China-based Integrity Technology Group, which they say holds Chinese…
-
An IDCF Cloud ransomware attack has disrupted services used by 495 companies and local governments in Japan. Operator IDC Frontier shut down affected infrastructure after detecting the incident in its East Japan Region 1 environment. The company says the attack began at 3:40 a.m. local time on October 7. Investigators are still determining how the…
-
Some low-cost Android smartphones have reached customers with Midnight Mimosa malware embedded in their firmware. The malicious software can silently install applications, generate fraudulent advertising activity and turn infected phones into residential proxies. Bitdefender researchers identified thousands of affected devices across more than 150 countries over roughly two years. Mexico, France, Italy, the United States,…