


Category: Cyber Security
-

The Yanluowang access broker case reveals how one individual enabled a series of ransomware attacks by selling entry into corporate networks. His guilty plea confirms the critical role that initial access brokers play in modern cybercrime and highlights the urgent need for stronger access-security practices across organisations. How the Broker Operated The broker, identified as…
-
The Samsung zero-day patch has become a priority after researchers confirmed that advanced spyware operators exploited a critical flaw in Samsung phones. CISA responded with an urgent directive that requires federal agencies to secure affected devices before attackers gain further advantages. The Zero-Day at the Center of the Directive Researchers identified the exploited bug as…
-
Quantum Route Redirect fuels large-scale phishing attacks against Microsoft 365 users by automating redirects, credential theft and visitor filtering. The Quantum Route Redirect platform shows how phishing-as-a-service models now use automation to increase reach and efficiency. The campaign spans dozens of countries and relies on compromised domains that appear benign during initial inspection. How the…
-
The APT37 data-wiping attack highlights how North Korean operators weaponise trusted Android features after stealing account credentials. The group uses spear-phishing to compromise victims, then triggers remote wipes through Find Hub to destroy evidence and obstruct recovery. How APT37 Gains Initial Access Attackers begin with targeted KakaoTalk messages crafted to resemble legitimate communication from Korean…
-
LLM fake language has become a major concern as advanced AI models generate credible but false information that spreads quickly online. These models increasingly influence public understanding, and their errors now carry serious consequences. Because people trust fluent language, fake content from AI tools can mislead individuals, organisations, and entire industries. Therefore, experts warn that…
-
The Samsung Galaxy spyware campaign has raised significant alarm after researchers uncovered an advanced operation that targeted popular Galaxy models. Attackers used a zero-day exploit delivered through ordinary image files. This method bypassed user interaction and enabled deep access to microphone, file, and communication data. Because Galaxy devices have a massive global footprint, the threat…
-

The intel engineer data theft incident has triggered a high-stakes lawsuit after the company accused a former employee of stealing thousands of confidential files. The case highlights growing concerns about insider threats and sensitive-data exposure during workforce transitions. It also raises questions about how tech firms manage access controls and monitor data movement when staff…
-
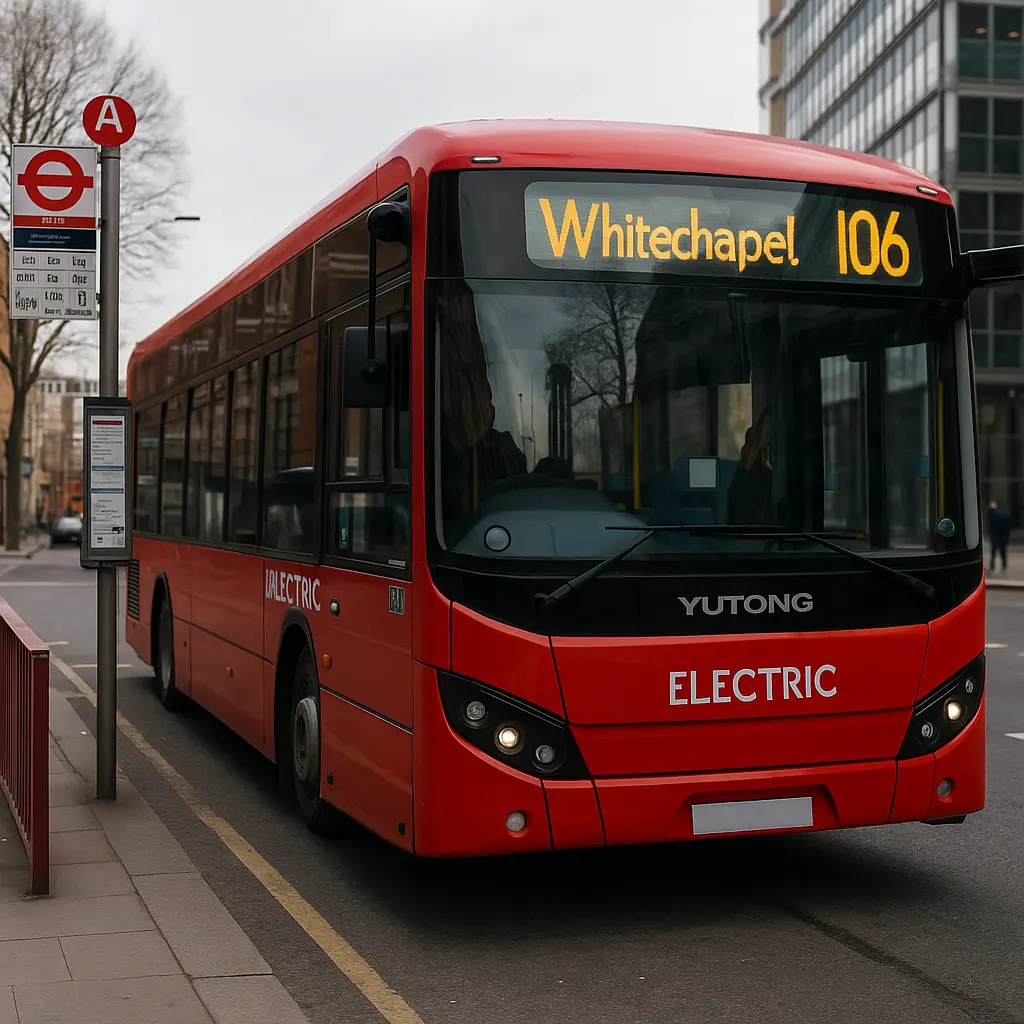
The UK government has opened a security review into Yutong electric buses after tests in Norway and Denmark suggested the vehicles may allow remote access to critical onboard systems. The findings raise concerns about digital control, software dependencies, and the cybersecurity posture of imported transport infrastructure. Why the Review Started Officials began investigating after Scandinavian…
-
NAKIVO Backup & Recovery v11.1 introduces a wide set of updates that strengthen disaster recovery, managed-service operations, and multi-platform data protection. The release targets organizations that need faster recovery, smoother MSP workflows, and more efficient backup across virtual, physical, and hybrid systems. Expanded multilingual support The platform now supports French, Italian, German, Polish, and Chinese…
-
runc flaws have created new concern in the container ecosystem after security researchers disclosed dangerous vulnerabilities that enable full escape attacks. These issues allow threat actors to break container isolation and execute code directly on host machines. The findings highlight the high impact of runtime weaknesses across Docker and other platforms that rely on runc…