

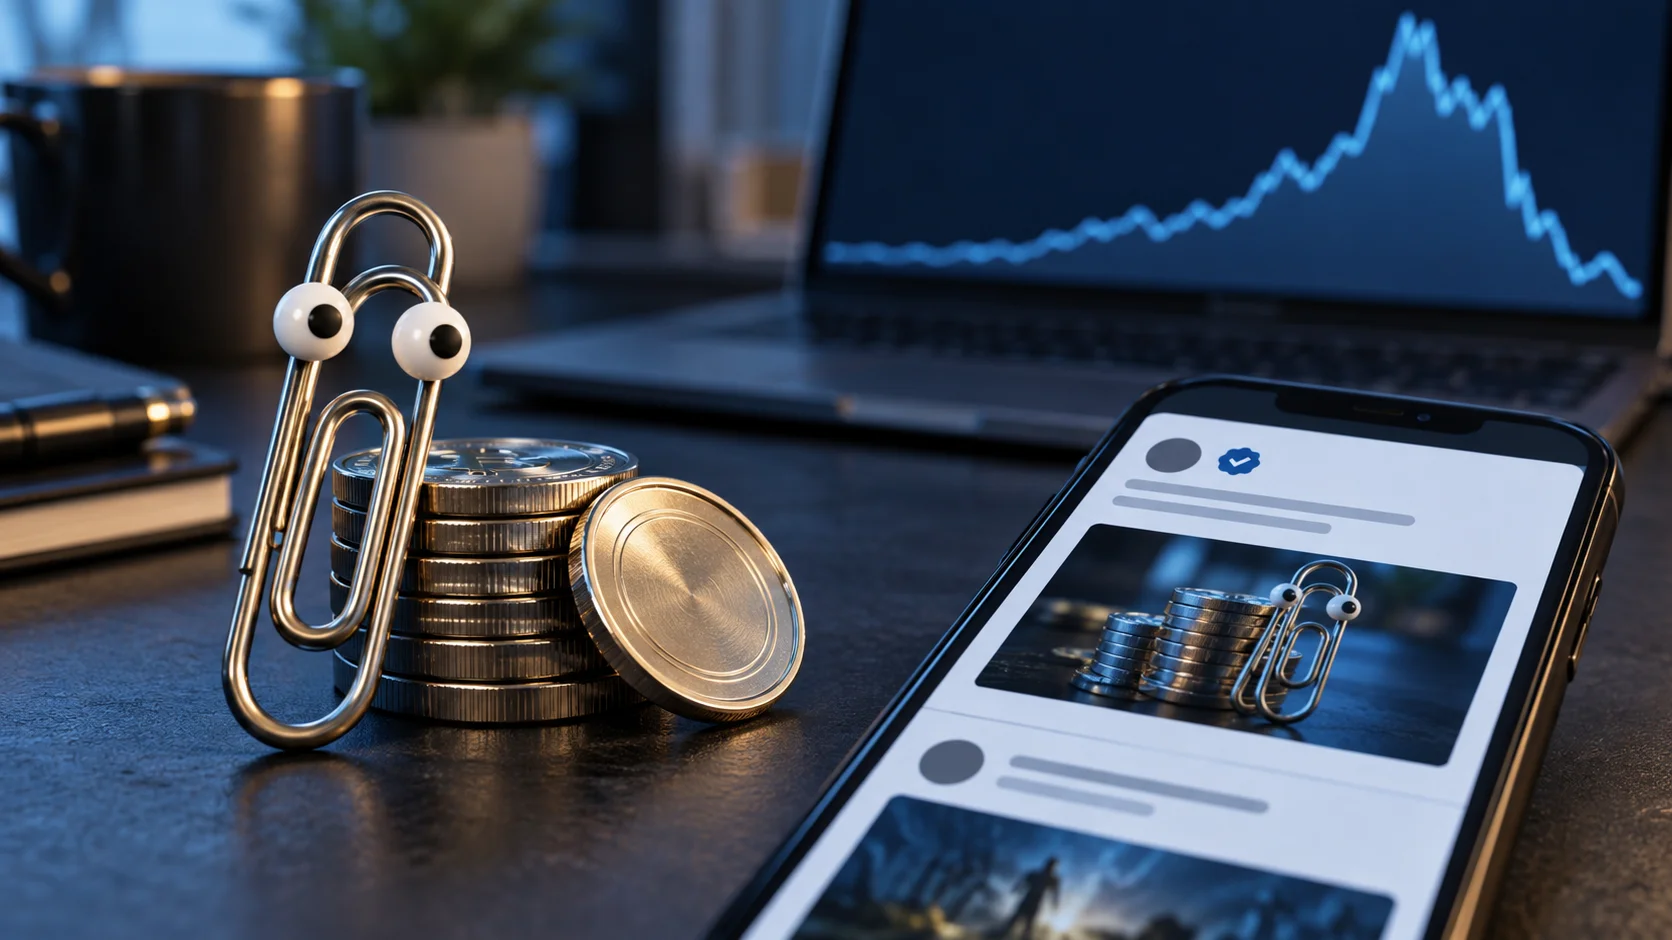
Microsoft has secured its official X account after attackers used it to promote an unauthorized cryptocurrency token linked to its Clippy character. The Microsoft X hack affected an account with more than 13 million followers, giving the promotion a large potential audience.
The company confirmed that someone accessed the account without permission and published posts that did not come from Microsoft. It has since removed the content and launched an investigation.
Hijacked Account Amplifies Clippy Impersonator
The incident unfolded on October 1, when Microsoft’s account followed and reposted content from an account impersonating its former virtual assistant.
That account, @clippymsftcto, subsequently received a suspension. However, another account, @ClippyMSFT, continued promoting a token called $Clippy after sharing the Microsoft repost.
The promotion claimed that the token had a liquidity pool paired with $MSFT. Microsoft rejected any connection between the project and its business, stock ticker or intellectual property.
The activity appeared consistent with a pump-and-dump scheme, in which promoters build interest in an asset before selling their holdings. However, the available information does not establish whether the attackers sold tokens or how much money anyone lost.
Microsoft Rejects Token Endorsement
Microsoft said it had restored control of the account and removed the unauthorized posts. Meanwhile, it continues to investigate how the attackers gained access.
In a separate, subsequently deleted statement, the company addressed the misuse of Clippy and Microsoft branding. It said it had not authorized, sponsored or endorsed the token.
The statement also rejected any affiliation with the token’s creators or related cryptocurrency project. Additionally, Microsoft said it would pursue appropriate legal action to seek removal of the unauthorized token and associated materials.
The company has not publicly identified the attackers or explained the method they used to compromise the account.
Earlier Microsoft India Breach Promoted Wallet Theft
The Microsoft X hack follows a separate compromise of the company’s India account in June 2024.
During that incident, attackers changed the account to impersonate Roaring Kitty, the online identity of trader Keith Gill. At the time, the account had more than 211,000 followers.
The attackers then promoted a supposed GameStop cryptocurrency presale through posts and replies. Those messages directed users to a malicious website.
People who connected their wallets and approved malicious transactions risked losing their cryptocurrency to a wallet-draining service. Unlike the latest Clippy promotion, that earlier campaign specifically used a fraudulent presale to lure users into authorizing transfers.
High-Profile Accounts Give Fraudulent Posts Credibility
Other prominent account breaches illustrate how attackers can exploit an established audience.
In January 2024, attackers compromised the US Securities and Exchange Commission’s X account through a SIM-swapping attack. They published a false announcement claiming approval of spot Bitcoin exchange-traded funds, briefly moving Bitcoin’s price.
Eric Council Jr. later pleaded guilty to his role in that conspiracy and received a 14-month prison sentence in 2025.
For Microsoft, the confirmed outcome so far is narrower: attackers published unauthorized cryptocurrency content, and the company regained control of its account. Questions about the initial access method, trading activity and potential financial losses remain unanswered.
0 responses to “Microsoft X Hack Pushes Unauthorized Clippy Crypto Token”